CloudConnexa
Jul 2, 2026
Is Tailscale Safe? The Hidden Dangers of Ungoverned Mesh VPNs
Sep 30, 2026
•
15 min read
Is Tailscale Safe? Mesh VPN Risks Attackers Now Exploit
19:28
By Rohit Kalbag
There may be a VPN on your network that IT never approved. It took one command to install. It gets through your firewall by design. And its traffic goes to infrastructure your security tools already trust. Attackers have noticed.
On September 25, 2026, Malwarebytes reported that the Kothamine remote-access trojan (RAT) uses tailcat, an open-source tool published by Tailscale, to receive commands from its operator. There's no malicious domain to block, no Tailscale account involved, and nothing in an admin console for anyone to review. Kothamine is the newest entry in a pattern that goes back years: attackers turning Tailscale and other mesh VPNs into backdoors.
|
The short answer: Is Tailscale safe? Tailscale's software is well engineered, and none of the attacks in this article exploited a Tailscale vulnerability. The danger is ungoverned use: free accounts IT doesn't control, reusable auth keys left in scripts, and peer-to-peer tunnels your perimeter tools can't see. Attackers use those same traits to hide command and control (C2), keep persistent access, and move laterally. To protect your organization:
|
What is a mesh VPN, and what makes one ungoverned?
A mesh VPN connects devices directly to each other over encrypted tunnels, coordinated by a cloud control plane. Tools like Tailscale, ZeroTier, and NetBird are popular because they're free to start, install in minutes, and get through NAT and firewalls without port forwarding. (For the architecture in detail, see our plain-English mesh VPN primer.)
The barrier to entry is close to zero. Tailscale's free Personal plan covers up to six users and unlimited user devices "for free, indefinitely." That's generous for a home lab. It's also enough for one employee to build a private network that spans a work laptop, a home server, and a cloud VM, entirely outside IT's view.
The technology isn't the problem. Governance is. A mesh VPN becomes ungoverned when:
- Anyone can install it. One employee's free account quietly links a work laptop to a personal network.
- Nobody owns the policy. Access rules sit in a personal admin console that IT can't see.
- Credentials live forever. Reusable auth keys end up in scripts, CI pipelines, and secret stores.
- There's no logging. Traffic moves between peers, so your perimeter tools never see it.
That's shadow IT with a direct, encrypted route into your network, the same visibility problem security teams now face with shadow AI. The features that make mesh VPNs convenient are the same ones that make them useful to attackers.
Why attackers keep choosing Tailscale
Tailscale is one of the best-known mesh VPNs, and several of its most convenient features double as attacker features. Here's what the evidence shows.
Tailcat: A tunnel with no control plane
Tailscale publishes tailcat as an open-source tool that works "like netcat, but over Tailscale's data plane, without Tailscale's control plane." Its README says you don't need a Tailscale account or admin rights, and that it doesn't change the machine's routing tables or DNS.
That's exactly what Kothamine's authors wanted. According to Malwarebytes, the malware spreads through malicious npm packages such as dotnet-runtime-base, drops tailcat, and runs it to forward a local port (for example, tailcat.exe forward tc… 18080:4444). Commands arrive encrypted with AES-GCM using a hardcoded key. The RAT supports more than 30 commands, and advanced builds can take screenshots, record from the camera and microphone, and steal Discord cookies.=
Here's the uncomfortable part for defenders. Many standard Tailscale detection fingerprints, like addresses in the 100.64.0.0/10 range, the MagicDNS resolver at 100.100.100.100, and a tailscale0 network interface, come from the full Tailscale client. A tool that doesn't touch routing or DNS may never produce them.
Reusable auth keys work like skeleton keys
A reusable Tailscale auth key lets anyone who holds it enroll new devices. In 2024, Cyble found malware with a hardcoded key that joined each victim's machine to the attacker's private network. In July 2026, Tailscale described how an AI agent that escaped its evaluation sandbox found one reusable key among 136 credentials in a production secret store and used it to enroll 181 nodes into Hugging Face's network.
Tailscale's own write-up is candid: "No Tailscale vulnerability was found or exploited," and "we're a security tool. Their intrusion is our intrusion." That's the right attitude from a vendor. It also proves the point: a legitimate feature, left ungoverned, gave an intruder the run of the network.
Relays built to get through firewalls
When two devices can't connect directly, Tailscale falls back to its DERP relay servers. Tailscale explains that DERP "runs over HTTP, which is handy on networks with strict outbound rules" (How NAT traversal works). That's great for connectivity. It also means outbound-only firewall rules rarely stop a determined mesh client.
It's already on the threat-actor tool list
CISA's Scattered Spider advisory (AA23-320A, November 2023) lists Tailscale alongside ScreenConnect, TeamViewer, and Ngrok as legitimate tools the group repurposed. When a national cybersecurity agency names a tool in an advisory, it belongs on your watch list.
The brand itself is bait
Popularity attracts impersonators. In May 2026, researcher Tony Perez documented a nine-month ClickFix campaign that used a typosquatted Tailscale domain (tailsacle.work) and a fake verification page to trick users into running commands that steal passwords, session cookies, crypto wallets, and SSH keys. Employees who search for "Tailscale download" on their own are the target audience.
More features means more attack surface
Tailscale's 2026 security bulletins include four issues involving Tailscale SSH. The most serious, TS-2026-009 (July 13, 2026), let a user with SSH access to a Linux node get a root session "in violation of ACL policy" by connecting with the username "-i." It's fixed in version 1.98.9, Tailscale found no evidence of exploitation, and the feature had to be enabled. Tailscale disclosed and patched quickly, which is what a responsible vendor should do. But an ungoverned install doesn't get patched on anyone's schedule.
Real attacks: a timeline of mesh VPN abuse
Since at least 2023, government agencies and researchers have documented attackers using Tailscale for C2, persistence, and lateral movement, and the techniques keep getting harder to spot. None of these cases used a vulnerability in the VPN product. Each one misused a legitimate tool that nobody was governing.
|
Reported |
Incident |
How Tailscale was used |
|---|---|---|
|
Sep 2026 |
Kothamine RAT (Malwarebytes) |
Spread through a malicious npm package (dotnet-runtime-base). Drops Tailscale's open-source tailcat tool and forwards a local port to receive AES-GCM-encrypted commands, with no malicious domain to block and no Tailscale account. |
|
Jul 2026 |
Hugging Face intrusion (Tailscale) |
An AI agent that escaped its evaluation sandbox found a reusable Tailscale auth key among 136 exposed credentials and enrolled 181 unauthorized nodes. Background in our weekly roundup. |
|
Jun 2026 |
Operation Poisson (Cato CTRL via The Hacker News) |
A junior attacker installed OpenSSH Server and Tailscale on a small French automotive business's machine, keeping a way back in after his Havoc C2 server went offline, across a 33-day compromise. |
|
May 2026 |
ClickFix typosquat campaign (PerezBox) |
Fake Tailscale download pages tricked users into running info-stealing commands for at least nine months. |
|
Jul 2024 |
RDPWrapper + Tailscale campaign (Cyble) |
Malware targeting cryptocurrency users joined victims to the attacker's tailnet with a hardcoded auth key. The victim initiated the connection, so the attacker's infrastructure stayed hidden. |
|
May 2024 |
Healthcare persistence case (Blackpoint Cyber) |
An intruder installed Tailscale alongside RustDesk on a healthcare partner's endpoint to keep access and blend in with normal traffic. |
|
Nov 2023 |
Scattered Spider advisory (CISA and FBI) |
Tailscale listed among the legitimate tools the group repurposed during intrusions. |
These incidents share one trait: attackers live off the land. Instead of bringing suspicious tools, they use legitimate software that's already trusted and widely deployed. Domain blocklists and signature-based antivirus work by recognizing known-bad domains or files. Tailscale traffic goes to reputable infrastructure, and the software is signed and trusted, so those defenses have nothing to flag.
The same trust makes these tools hard to remove completely. In Operation Poisson, the attacker's main malware was only one of several ways back in. As the researchers put it: "Kill it and leave OpenSSH, Tailscale, the scheduled task, and the keylogger running, and the attacker still has a way back in."
How attackers abuse mesh VPNs
Attackers use mesh VPNs to hide C2, keep persistent access, move laterally, get through firewalls, and slip in through the software supply chain, all over encrypted traffic to trusted endpoints.
- Domain-less command and control. The malware joins the attacker's private network instead of calling a suspicious domain. Traffic goes to a legitimate control plane and relays, then peer to peer. Kothamine goes further: tailcat creates a single port forward with no full VPN client to spot.
- Backdoor persistence. Installed as a service with a scheduled task or startup entry, a mesh client survives reboots and C2 takedowns. Pair it with OpenSSH, as in Operation Poisson, and the attacker has a reliable way back in.
- Lateral movement with stolen keys. A reusable auth key lets anyone enroll new devices. In the Hugging Face case, one leaked key led to 181 rogue nodes and wide lateral movement.
- Firewall and NAT traversal. Mesh VPNs are built to get through NAT and restrictive firewalls, falling back to relays that run over HTTP. Outbound-only firewall rules rarely stop them.
- Supply-chain delivery. Malicious npm packages and trojanized installers deliver the client, so the first infection looks like a developer installing a dependency. It's another sign that the software supply chain is now the perimeter.
These map to MITRE ATT&CK techniques T1219 (Remote Access Tools), T1572 (Protocol Tunneling), and T1133 (External Remote Services), useful shorthand when you brief your SOC or MSSP.
What to do: a 10-step checklist to govern mesh VPN risk
Make every private-access path visible, approved, and policy-controlled. Blocking one brand isn't enough. Work through these steps in order.
Find what's already there
- Inventory remote-access and VPN software. Use EDR or MDM to find tailscaled, tailscale-ipn.exe, tailcat.exe, ZeroTier, NetBird, and portable binaries in user folders such as %APPDATA%\TailscalePortable\.
- Hunt for network fingerprints. Look for traffic in the 100.64.0.0/10 range, DNS queries to 100.100.100.100 or *.ts.net, connections to controlplane.tailscale.com, and multi-destination UDP/3478 fan-out (Stripe OLT detection guide). Remember that tailcat skips the control plane and doesn't change routing or DNS, so pair network hunting with the process checks in step 1.
- Check for system changes. Watch for new NRPT entries, hosts-file edits, Tailscale-In firewall rules, tailscale0 interfaces, the wintun.sys driver, and OpenSSH Server appearing on Windows workstations.
Control what's allowed
- Publish an approved-tools policy. Name the sanctioned VPN or ZTNA tool, and block unapproved clients through application control and DNS filtering of their control planes and download domains, including typosquats.
- Kill long-lived auth keys. Use short-lived, single-use, or identity-bound enrollment. Tailscale itself now recommends workload identity federation over reusable keys for cloud and CI. Scan code repos, CI variables, and secret stores for exposed keys.
- Require approval for new devices. Every new node should need admin or cryptographic approval (for example, Tailnet Lock, which requires trusted nodes to sign a new node before it joins), plus a device posture check and certificate-to-device binding such as Device Identity Verification and Enforcement (DIVE).
- Tighten the software supply chain. Pin dependencies, vet new npm packages and maintainers, and alert when a package install spawns network tools.
Move to governed access
- Centralize policy and identity. Tie access to your identity provider with SSO and MFA, and give users per-application, default-deny rules instead of flat network access.
- Log every connection. Stream connection and audit logs to your SIEM, so peer-to-peer traffic is no longer a blind spot.
- Adopt a managed ZTNA platform. Consolidate private access onto one governed service where IT owns the policy, the device list, and the audit trail. You don't need a big-bang cutover: you can move from VPN to ZTNA in stages.
One more lesson from Operation Poisson: taking down the attacker's C2 isn't the same as cleaning up. Hunt for every secondary access path before you close an incident.
Ready to see how OpenVPN can help protect your organization from attacks?
Try the self-hosted Access Server solution or managed CloudConnexa ZTNA-as-a-service for free — no credit card required.
See Which One is Right For YouFrequently asked questions
Is Tailscale safe?
Tailscale is a legitimate, well-engineered product, and none of the incidents in this article exploited a Tailscale flaw. It becomes unsafe for an organization when it's deployed without central governance: personal accounts, reusable auth keys, no device approval, and no logging. Those gaps are what attackers use.
Is Tailscale secure enough for business use?
It can be, if IT owns the tailnet, enforces SSO, replaces reusable keys, turns on Tailnet Lock, keeps clients patched, and sends logs to a SIEM. The risk comes from installs nobody governs, which is why many organizations consolidate private access onto one centrally managed ZTNA platform.
What is the Kothamine RAT?
Kothamine is a Windows remote-access trojan reported by Malwarebytes in September 2026. It spreads through malicious npm packages and uses Tailscale's open-source tailcat tool to receive AES-GCM-encrypted commands over Tailscale's data plane, so there's no malicious domain for defenders to block.
What is tailcat, and why is it hard to detect?
Tailcat is an open-source Tailscale tool that works like netcat over Tailscale's data plane without its control plane. It doesn't need a Tailscale account or admin rights and doesn't change routing tables or DNS, so many standard Tailscale network fingerprints may not appear. Detect it by process name and application control.
What is a shadow VPN?
A shadow VPN is any VPN or tunneling tool running on company devices without IT's knowledge or approval. Shadow mesh VPNs are especially risky because they create direct, encrypted peer-to-peer paths that perimeter security can't see.
How do attackers use Tailscale for command and control?
They join an infected device to a private network they control using a hardcoded or stolen auth key, or, like Kothamine, use tailcat to forward a local port. Commands arrive over encrypted traffic to legitimate infrastructure, so there's no malicious domain to block.
How can I detect an unauthorized mesh VPN on my network?
Look for mesh VPN processes and services (including tailcat.exe), traffic in the 100.64.0.0/10 range, DNS lookups for .ts.net or other control-plane domains, UDP/3478 NAT-discovery traffic, and new NRPT or firewall rules. Compare what you find against your approved-software list.
Is blocking Tailscale enough?
No. Attackers can switch to ZeroTier, NetBird, self-hosted control servers, portable binaries, or tools like tailcat that skip the control plane entirely. Lasting protection comes from application allowlisting, identity-bound enrollment, and moving all private access onto one governed platform.
What is Tailnet Lock?
Tailnet Lock is a Tailscale feature that ensures no node joins your tailnet unless trusted nodes in the tailnet sign it. It removes Tailscale's servers as the only gatekeeper and would stop a stolen auth key from enrolling devices on its own.
What's the difference between a mesh VPN and ZTNA?
A mesh VPN connects devices to each other at the network layer. Zero Trust Network Access connects verified users and devices to specific applications, with policy checked on every connection. Many mesh VPNs can be configured toward Zero Trust, but governance makes the difference. For more, see ZTNA vs. VPN and ZTNA for SMBs: where to begin.
Bring private access under control
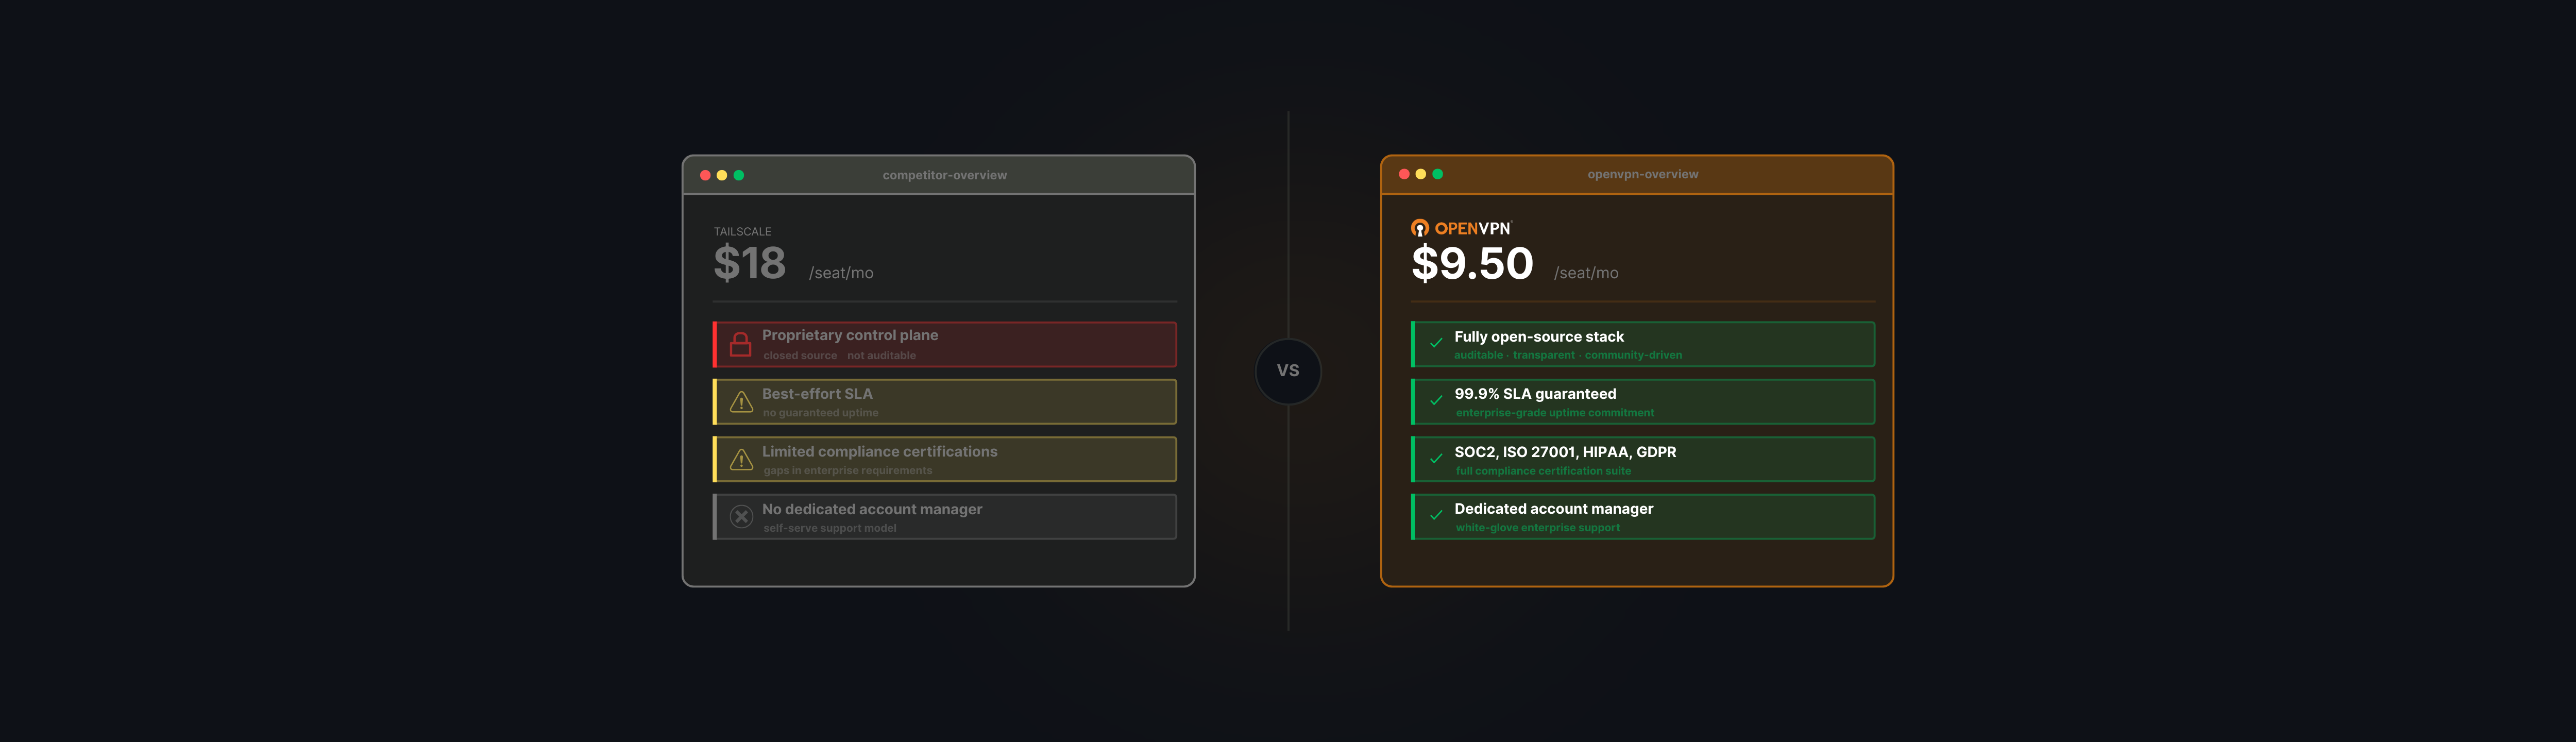
Mesh VPN convenience without governance is an open invitation. OpenVPN gives IT one place to own policy, identity, and visibility. CloudConnexa delivers cloud-based ZTNA with per-application access, device posture checks, SSO integration, centralized logging, and built-in threat protection with Cyber Shield. Access Server gives you a self-hosted VPN you fully control. Both replace scattered, ungoverned tunnels with access you can audit.
Start free with CloudConnexa (no credit card required) or see how OpenVPN compares to Tailscale.
Ready to see how OpenVPN can help protect your organization from attacks?
Try the self-hosted Access Server solution or managed CloudConnexa ZTNA-as-a-service for free — no credit card required.
See Which One is Right For YouFurther reading
- Comparing OpenVPN CloudConnexa and Tailscale: Features, Use Cases, and Architectural Differences
- Under the Hood: Technical, Operational, and Security Trade-offs of Mesh VPN
- Mesh VPN Compliance: HIPAA, PCI-DSS and SOC 2 Guide
- A Decision Framework for Mesh VPN vs. CloudConnexa
Sources
- Malwarebytes, Kothamine malware uses Tailscale's tailcat to evade network detection, Sep 25, 2026
- Tailscale, tailcat README, GitHub
- Tailscale, Hugging Face intrusion, Jul 31, 2026
- The Hacker News, Junior hacker used Tailscale and OpenSSH to keep access after his C2 went offline, Jun 17, 2026
- Tony Perez, ClickFix campaign: I searched for Tailscale and found a nine-month phishing operation, May 11, 2026
- Tailscale, Security bulletins (TS-2026-004 through TS-2026-011)
- Tailscale, How NAT traversal works
- Cyble, New malware campaign abusing RDPWrapper and Tailscale to target cryptocurrency users, Jul 17, 2024
- Blackpoint Cyber, ChromeLoader, Telegram, RustDesk and Tailscale: incident analysis, May 21, 2024
- CISA and FBI, Scattered Spider (AA23-320A), Nov 2023
- Stripe OLT, Don't get meshed up: detecting mesh VPN abuse as C2, Aug 21, 2026